Access control
What a connected client may do, decided by its credential and by the switches on Connect: reach, level, the profile tick, confirmation, and revocation.
A connected AI can do exactly what its credential allows, and the credential is the person’s: they minted it or approved it, and they change it on the Connect page without touching the client. Every rule below is enforced on the server, on the credential’s next call; nothing here depends on the client behaving.
Two credentials, two ceilings
Section titled “Two credentials, two ceilings”| Consent (an app connected over MCP) | Developer key (the skill, a header, code) | |
|---|---|---|
| Ceiling | read-only, always | the key’s level: Read, Read & write, Full access |
| Reach | the Memories ticked on consent, switchable later | the Memories ticked on the key, or all including later ones |
| Profile | read, when Profile access was ticked on the consent screen | when Your profile was ticked: read, and at higher levels keep or forget a statement |
| Confirmation | is not offered a delete or forget at all | can, with confirm=true at Full access |
| Ends | Disconnect… on the app’s page, per credential under Approvals, or expiry after 90 days (the tile then says Approval expired · authorize again) | Revoke…, or expiry |
An app that needs to write does not get a wider consent; the person mints a key for it instead, and the key says how wide.
Reach is the list of Memories a credential may use. It has one state and three views of it: the Uses card on the client’s page in Connect, the Use in card on the Memory’s page, and the Memory access switches on a key’s page. Off takes effect on the very next call.
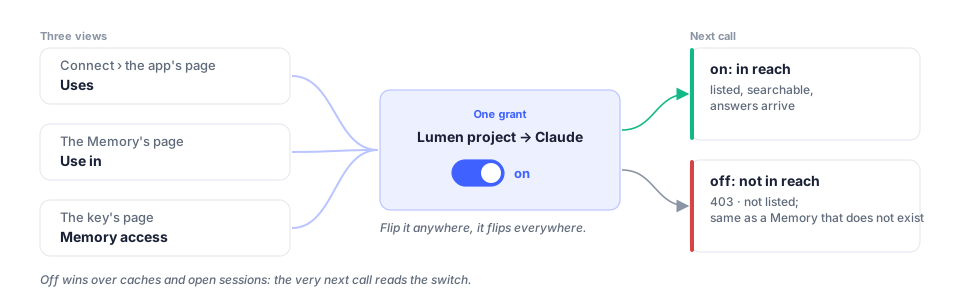
No call names a Memory: searches and lists cover the Memories in reach and leave the others
out, and an id from a Memory outside the reach answers 404, the same as one that does not
exist, over MCP and REST alike. get_capabilities (GET /v1/capabilities) does not list it.
A client cannot tell withheld from absent, and cannot ask for more; only the person can switch
it on.
The tool list is the grant
Section titled “The tool list is the grant”tools/list is filtered per caller. A consent-minted client is offered get_capabilities,
search_memories, list_memories, get_memory, the media reads and, when ticked,
list_profile_facts, and nothing that writes; a key is offered the tools of its level; a
marketplace buyer’s credential is offered get_capabilities and ask_memory alone. A model
cannot call what it was not offered, and a call that bypasses the list is refused anyway: over
MCP as a tool error (token missing required scope, or not in this agent’s capability
profile), over REST as 403 unauthorized. The table per credential is on
Any MCP client, and per level on
Authentication & Scopes.
Destructive verbs
Section titled “Destructive verbs”forget_memory, delete_document, delete_media and forget_profile_fact exist only at
Full access, and even there they do not execute on a bare call: without confirm=true
nothing changes and the answer is 428 confirmation_required (over MCP, a tool error with the
same code) with a how sentence for the model to relay. A consent-minted client is never offered
these verbs, and a call is refused (a tool error, token missing required scope; 403 over
REST) rather than answered with the sentence. From a Full access key, confirm=true counts as
the owner’s confirmation, which is why the skill tells the AI to pass it only after the
person agreed.
Deleting a Memory, a source’s material or the account has no agent-protocol verb at all; those belong to the owner’s session, in the app.
The profile
Section titled “The profile”The profile is about the person, not a topic, so it is granted separately from reach. It is
a list of standing statements (name, role, lasting preferences). A client offered
list_profile_facts reads them; one that was not ticked is not offered any profile tool. On a
key the tick is Your profile, changeable later on the key’s page, and what it grants
follows the key’s level: reading at Read, keeping a statement (add_profile_fact) at Read &
write, forgetting one (forget_profile_fact, with confirm=true) at Full access. A key minted
before the profile became a list holds the read only until the owner changes the key. On a
consent connection it is Profile access, set only on the consent screen: to change it,
Disconnect… the app and authorize it again.
Revocation
Section titled “Revocation”- Disconnect… on a client’s page revokes every credential that client holds, at once.
- Revoke under Approvals ends one credential when a client holds several.
- Revoke… on a key ends it at once; it stays listed for thirty days.
- Removing the connector inside the client does not tell Membase. Revoke on Connect to be sure.
Revocation and permission changes apply to subsequent requests. They do not remove content an external client has already received. A revoked key must be replaced with a new key; reconnecting an app requires a new authorization.
Seeing what a client did
Section titled “Seeing what a client did”A client’s page on Connect shows its last activity. A key’s page shows Usage (calls, refusals, the tool it calls most) and Recent activity (each call: tool, Memory, what came back, when; a refused call in red with the reason). A refusal is the sign that a client asked for a Memory or a verb it does not have, which is usually the person’s cue to widen it or to leave it.
Rules the skill teaches the model
Section titled “Rules the skill teaches the model”Because the server enforces the ceiling, the skill’s rules are about behaving well beneath
it: list the profile facts first when they are granted; search before answering about the
person’s past work; cite the Memory a result came from (memory_name); save only what the person supplied; never
pass confirm on the model’s own initiative; treat 403 as withdrawn access and ask the
person rather than retry.